Role and information boundaries
Design access around the people and records involved. Identify the information a role needs and the actions it may take.

Operate
Connect access, human accountability and operational visibility across intelligent work. Agree the information boundaries, architecture and responsibilities needed for the organization’s specific environment.
A governance design model. Specific access controls and operating responsibilities must be configured for the agreed application and deployment.
Design access around the people and records involved. Identify the information a role needs and the actions it may take.
Make consequential decisions accountable to an identified person or role. Connect the review point to the information and authority needed.
Use monitoring and reporting to make work understandable. Give the appropriate teams a view of active work and exceptions.
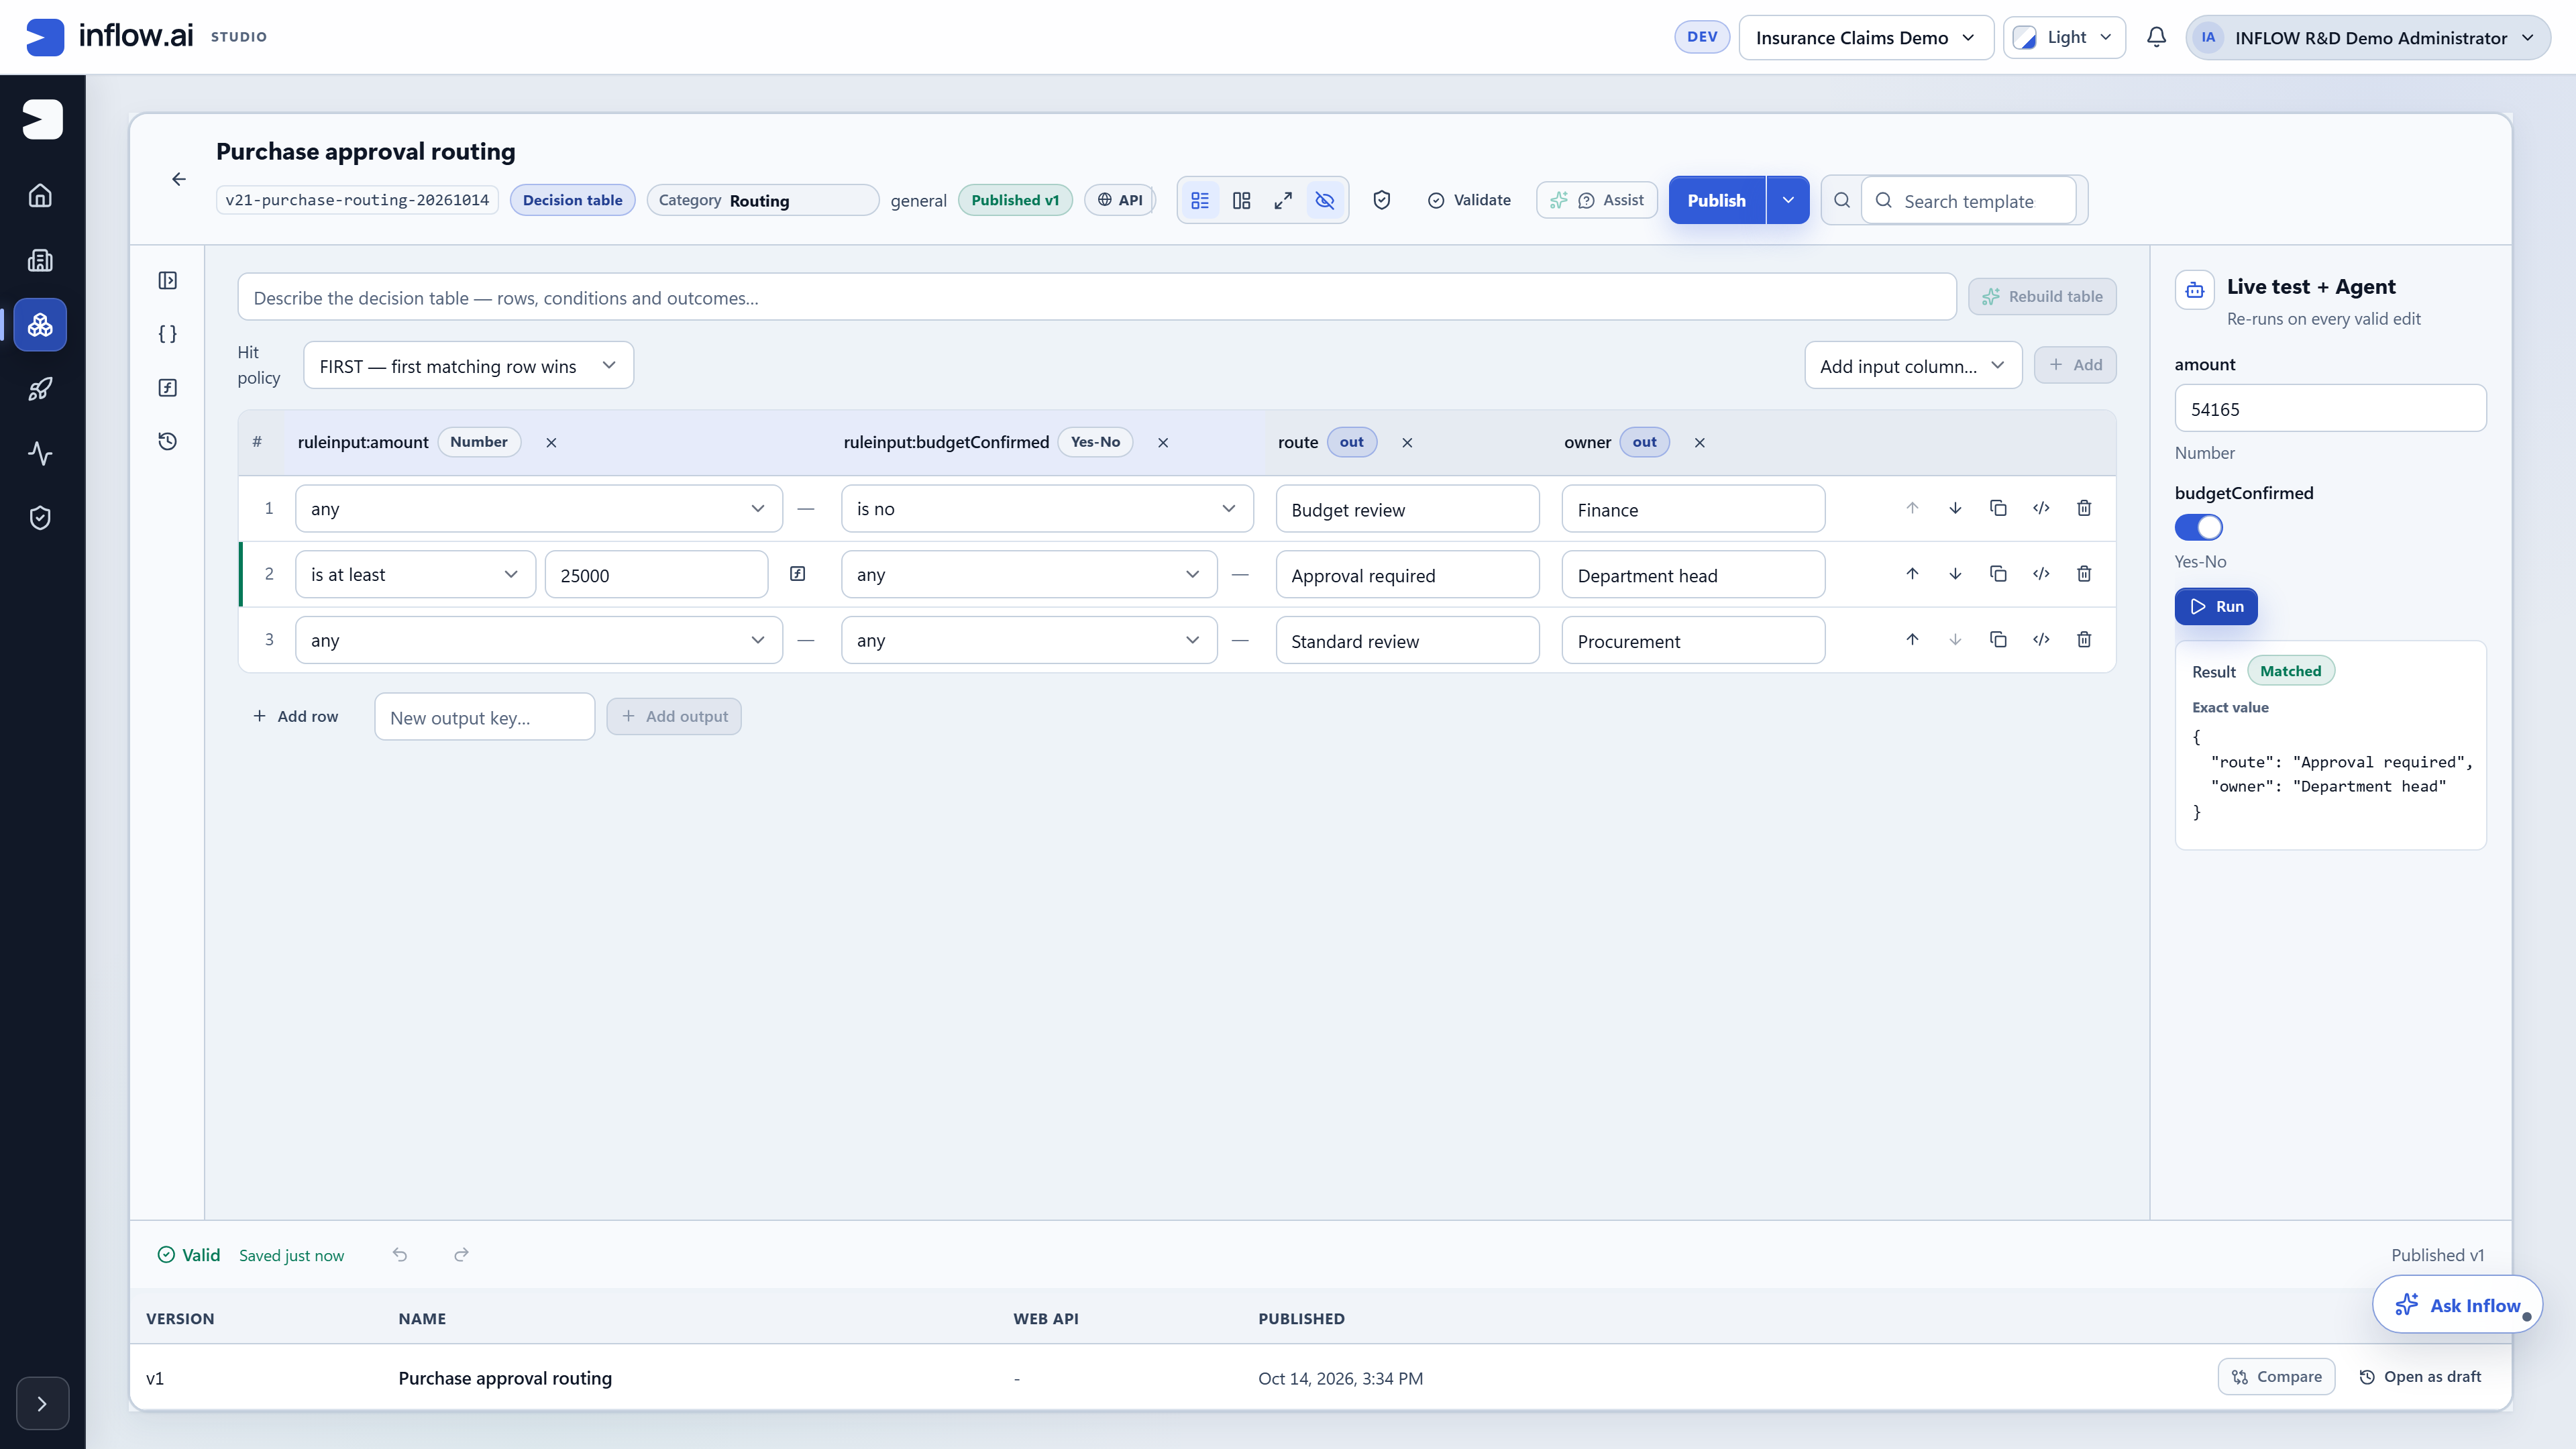
Treat changes to business logic and models as an explicit review concern. Retained editors show validation and version-related controls, without establishing a universal release-policy guarantee.
Align model use and information boundaries with organizational requirements. Confirm hosting, connectivity and support responsibilities for the specific engagement.
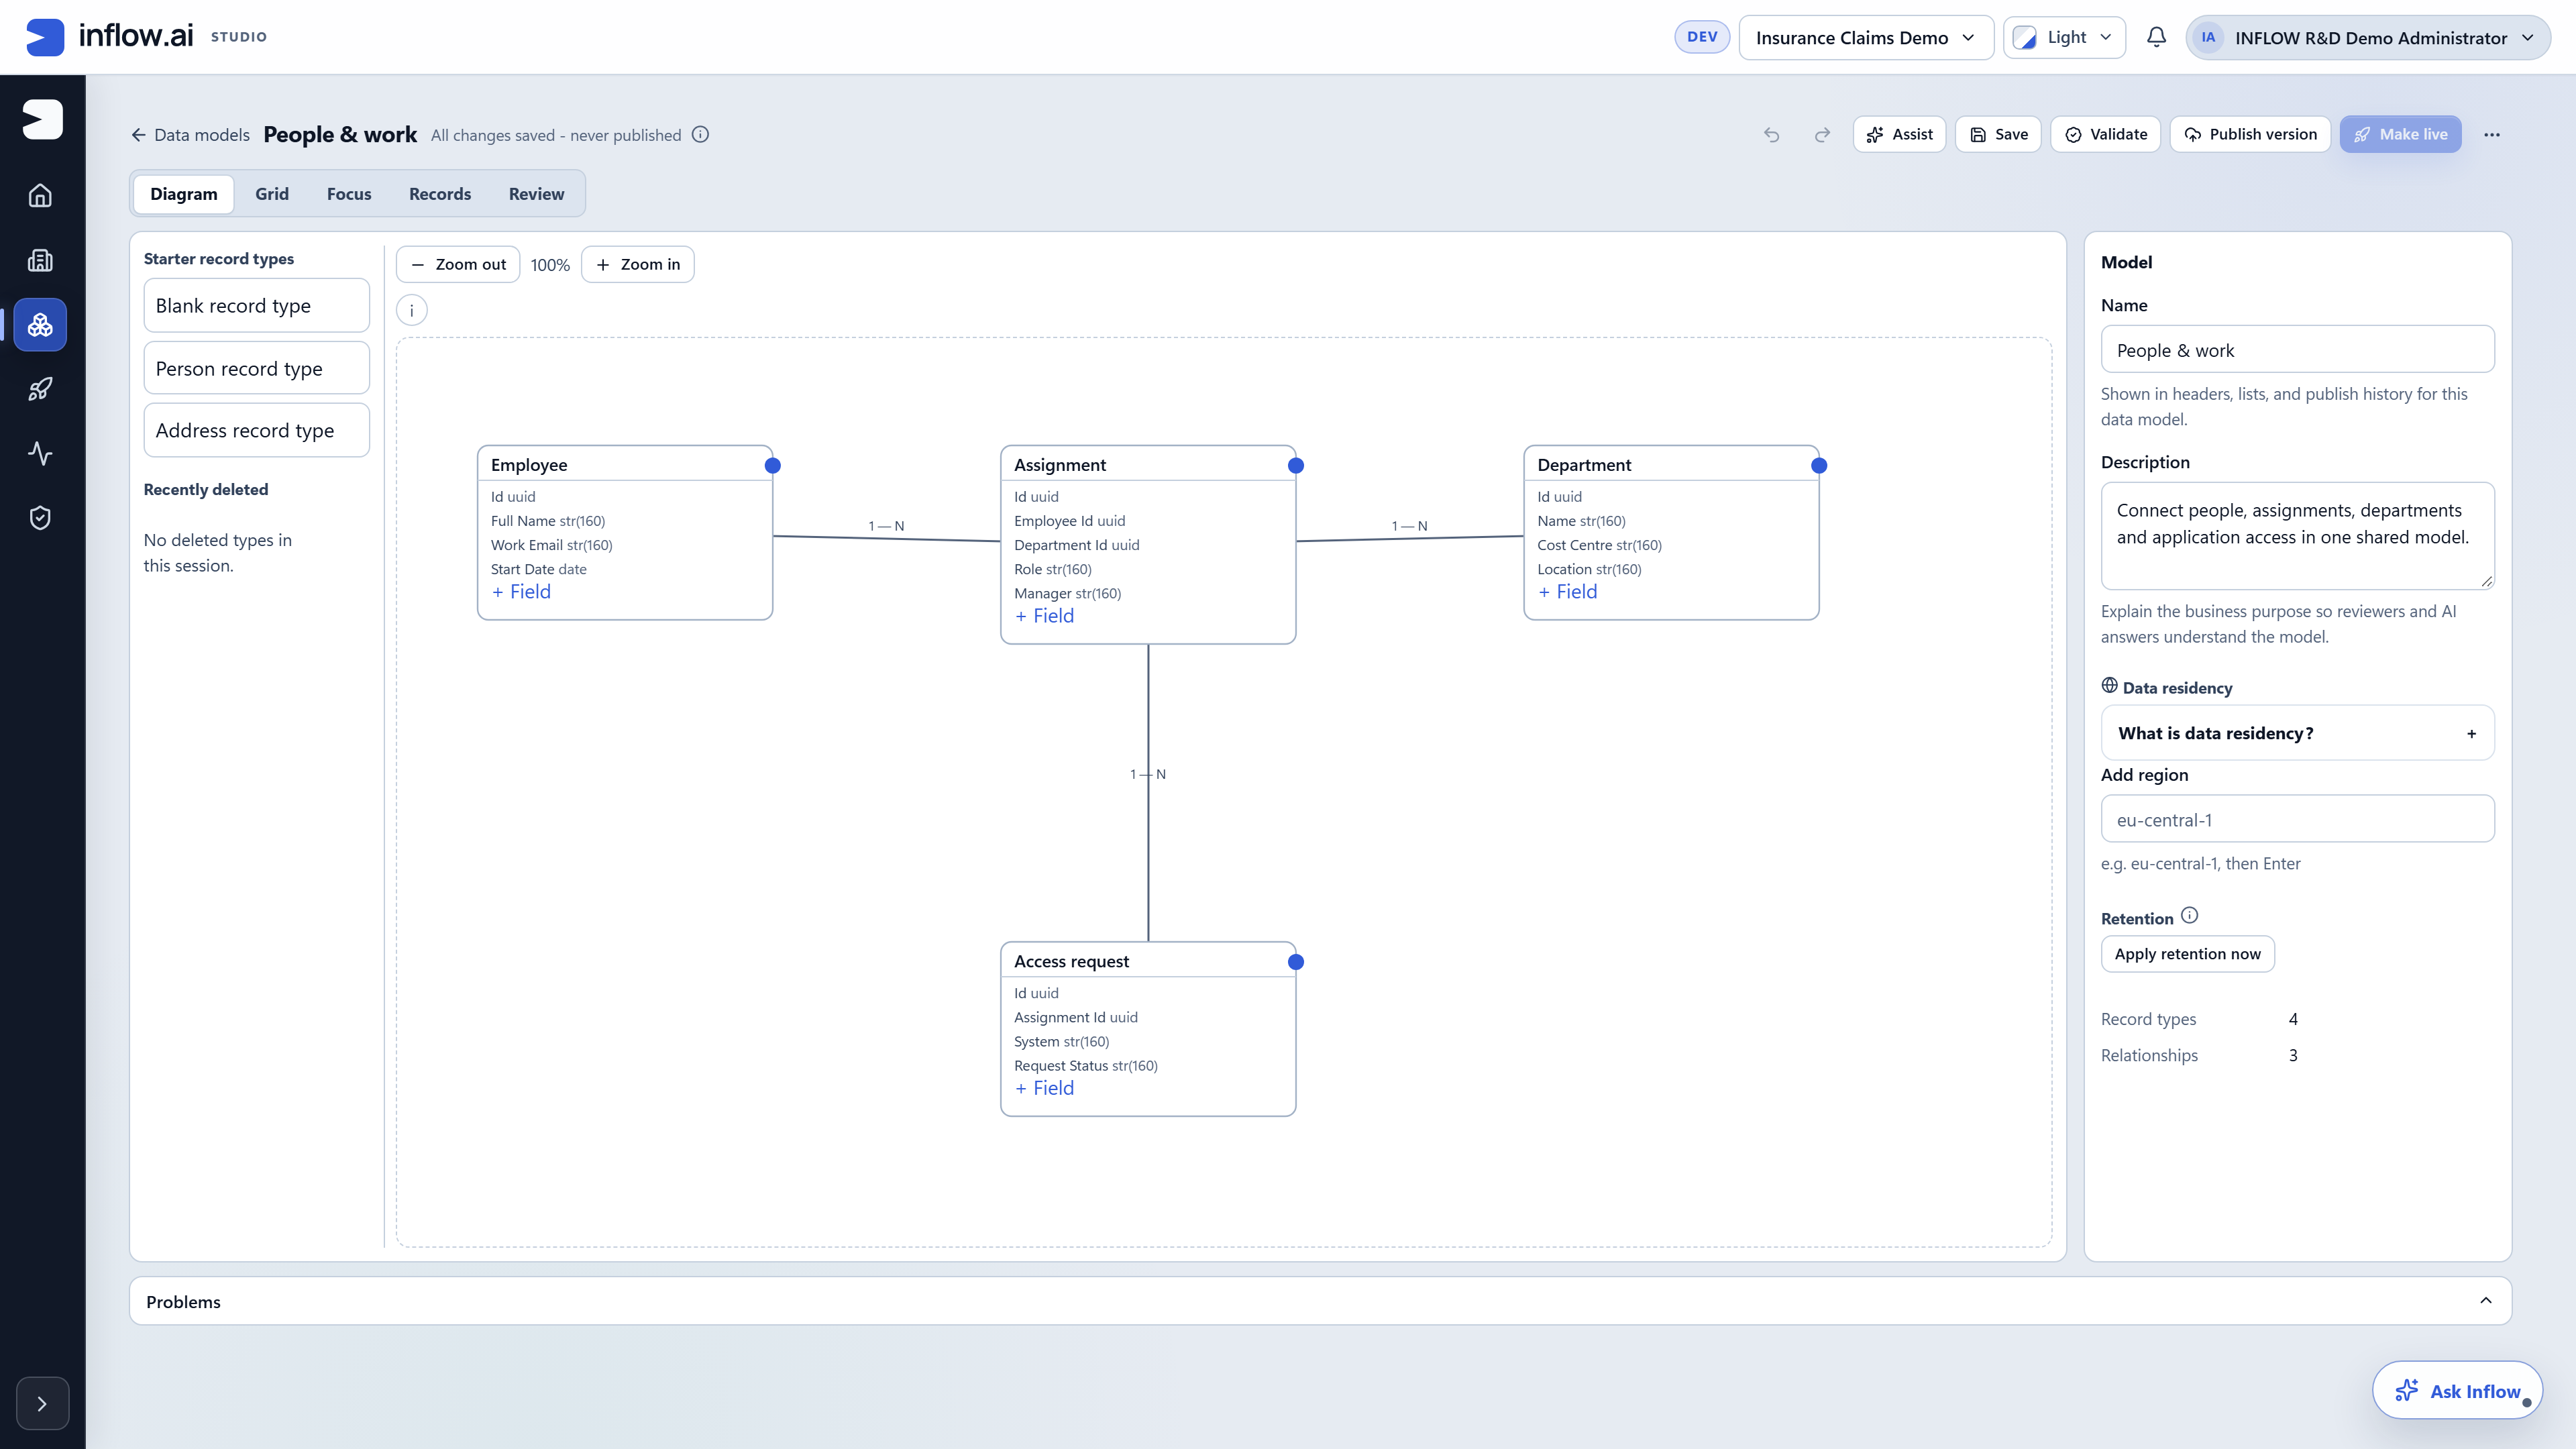
Evaluate data, AI, applications and orchestration together. Document where each responsibility and integration boundary sits before deployment.
Discuss the objects, responsibilities and boundaries that make this capability useful in your environment.
The access and regulatory requirements for your organization
The information, model and hosting boundaries of the solution
The review, audit and operating responsibilities to agree
Illustrative solution scenarios to shape a useful demonstration.
Agree who can access claim information and who can approve an outcome.
Review model connections and information boundaries with architecture stakeholders.
Define operating oversight for an application, its integrations and exception work.
Genuine retained demonstrations, shown with their original context. Open each view to inspect the details.
Bring your business journey, AI environment and integration needs. Let’s explore the right starting point.
Request a demo